How to Run a Security Awareness Program That Actually Changes Behavior
Annual training videos rarely change habits. Here is how a small business can run a light, year-round security awareness program that people remember and…
Equip your team with the knowledge they need to prevent cyber attacks. Our customized training programs cover essential cybersecurity best practices, such as password management, phishing awareness, and secure browsing. In addition, we create engaging security awareness materials, including videos, posters, and newsletters to keep your employees informed and vigilant.
Your people are your first line of defense. Our security awareness training equips your team with the knowledge they need to recognize and prevent cyber attacks, without drowning them in jargon or scaring them into inaction.
Every program is customized to your business. We cover essential cybersecurity best practices such as password management, phishing awareness and secure browsing, using real examples that look like the messages and situations your employees actually face.
Training does not stop when the session ends. We create engaging security awareness materials, including short videos, posters and newsletters, that keep good habits fresh and your employees informed and vigilant all year round.
Technology can block a lot of threats, but it cannot stop every convincing email, phone call or text message. Attackers know this, which is why so many incidents begin with a person being tricked into clicking a link, sharing a password or approving a payment. The FBI’s Internet Crime Complaint Center (IC3) consistently reports business email compromise among the costliest types of cybercrime it tracks, and those schemes rely on fooling people rather than breaking software.
The good news is that people can learn to spot these tricks. A team that knows what to look for, and feels comfortable reporting something suspicious, becomes an early warning system. In a small business, where one person may handle finance, HR and IT, that awareness is especially valuable.
That last habit matters most. Our training is built around the idea that reporting quickly is always the right move, and that nobody gets in trouble for asking.
Security training has a reputation for being dull, and much of it deserves that reputation. Long slide decks full of acronyms do not change behavior. We take a different approach: short sessions, real examples relevant to your industry and plain language that anyone in the company can follow, from the front desk to the founder.
We tailor examples to your business. A dental practice sees fake insurance and patient-record emails. An online store sees fake shipping notices and payment platform alerts. A professional services firm sees fake client document shares. When the examples look like the messages your team actually receives, the lessons stick.
Between sessions, we keep security visible with lightweight materials: a poster by the printer, a short monthly newsletter, a two-minute video that explains one habit at a time. Small, regular reminders work better than an annual marathon.
Key takeaways
Training should produce visible change. We include short knowledge checks to confirm understanding, and many clients pair training with our phishing simulation and testing service to measure how behavior changes over time. The metric we care about most is not who clicks, but how quickly people report suspicious messages. A rising report rate is one of the clearest signs of a healthy security culture.
Completion records are also useful evidence. Regulations and standards such as HIPAA and PCI-DSS expect organizations to train their workforce on security, and keeping simple records of who completed what, and when, makes audits, insurance applications and customer questionnaires easier to answer.
For individuals or very small teams who prefer to learn at their own pace, our self-paced Security Awareness for Everyone program covers the essentials. For more background, read how to build a security awareness program that works and how to spot phishing emails.
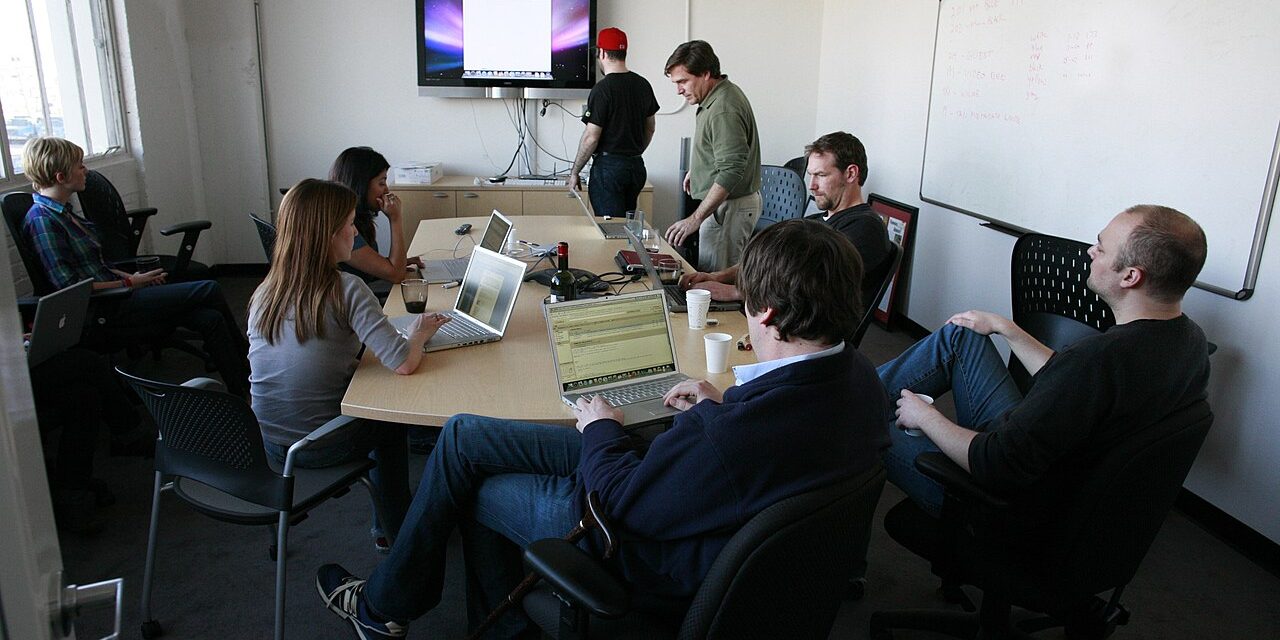
Interactive sessions, delivered remotely, built around your industry, your tools and the threats your team is most likely to see.
Practical guidance on password managers, passphrases, passkeys and multi-factor authentication, including how to handle suspicious login prompts.
How to spot suspicious emails, texts, calls and messages, with realistic examples and simple checks anyone can use.
Safe habits for websites, browser extensions, file downloads and public Wi-Fi, explained in plain language.
Simple rules for working from home or on the road, including device care, home networks and keeping work and personal use separate.
Focused guidance for finance, admin and leadership on business email compromise, fake invoices and payment-change requests.
A clear, blame-free process so employees know exactly what to do and who to tell when something looks wrong.
Branded posters, short videos and monthly newsletters that reinforce one habit at a time between training sessions.
We learn about your team, your tools, your industry and any recent incidents or close calls so the training addresses real risks.
We build a tailored program with examples drawn from your environment, choosing the topics and depth that fit each group of employees.
We deliver engaging live sessions, recorded for new hires and anyone who missed them, with short knowledge checks to confirm understanding.
We roll out posters, videos and newsletters on a simple schedule so security stays visible without becoming noise.
We review results, gather feedback and update the content as threats and your business change, so the program stays relevant.
Most live sessions run 45 to 60 minutes, which is long enough to cover the essentials and short enough to hold attention. We can split content into shorter sessions if that suits your team better.
Training is delivered remotely by default, which works well for distributed teams. Sessions are recorded so new hires and anyone who missed the live session can catch up.
Yes. Everyone gets the core essentials, and we add focused modules for higher-risk roles such as finance, HR, executives and anyone with administrator access.
We recommend training during onboarding, a refresher at least once a year, and short monthly reminders in between. Regular, bite-sized reinforcement is more effective than a single long session.
It can. HIPAA and PCI-DSS both expect security awareness training, and we provide completion records you can use as evidence. We are not a law firm, so please confirm specific legal obligations with your attorney.
Annual training videos rarely change habits. Here is how a small business can run a light, year-round security awareness program that people remember and…
A practical field guide to spotting phishing emails, texts and calls: a 30-second check, the red flags that matter most, and what to do…
What current NIST password guidance says, which MFA methods resist phishing, how passkeys work, and a four-week rollout plan small teams can actually follow.
Practical security awareness training that everyone on your team can understand, from the front desk to the founder. Short, friendly lessons build the everyday habits that…
A plain-English starting point for owners and managers who know security matters but are not sure where to begin. In about four hours you will put…

Secure your digital future today with SecuritySage - where cybersecurity meets simplicity, allowing you to focus on growth while we handle the rest.
Get Started